Certificaciones

Certification according to ISO standards is a guarantee that our company adheres to certain rules (whether laws or internal standards and regulations). We don’t change our procedures on a whim, but follow processes that guarantee consistent quality of the services we provide to our clients.

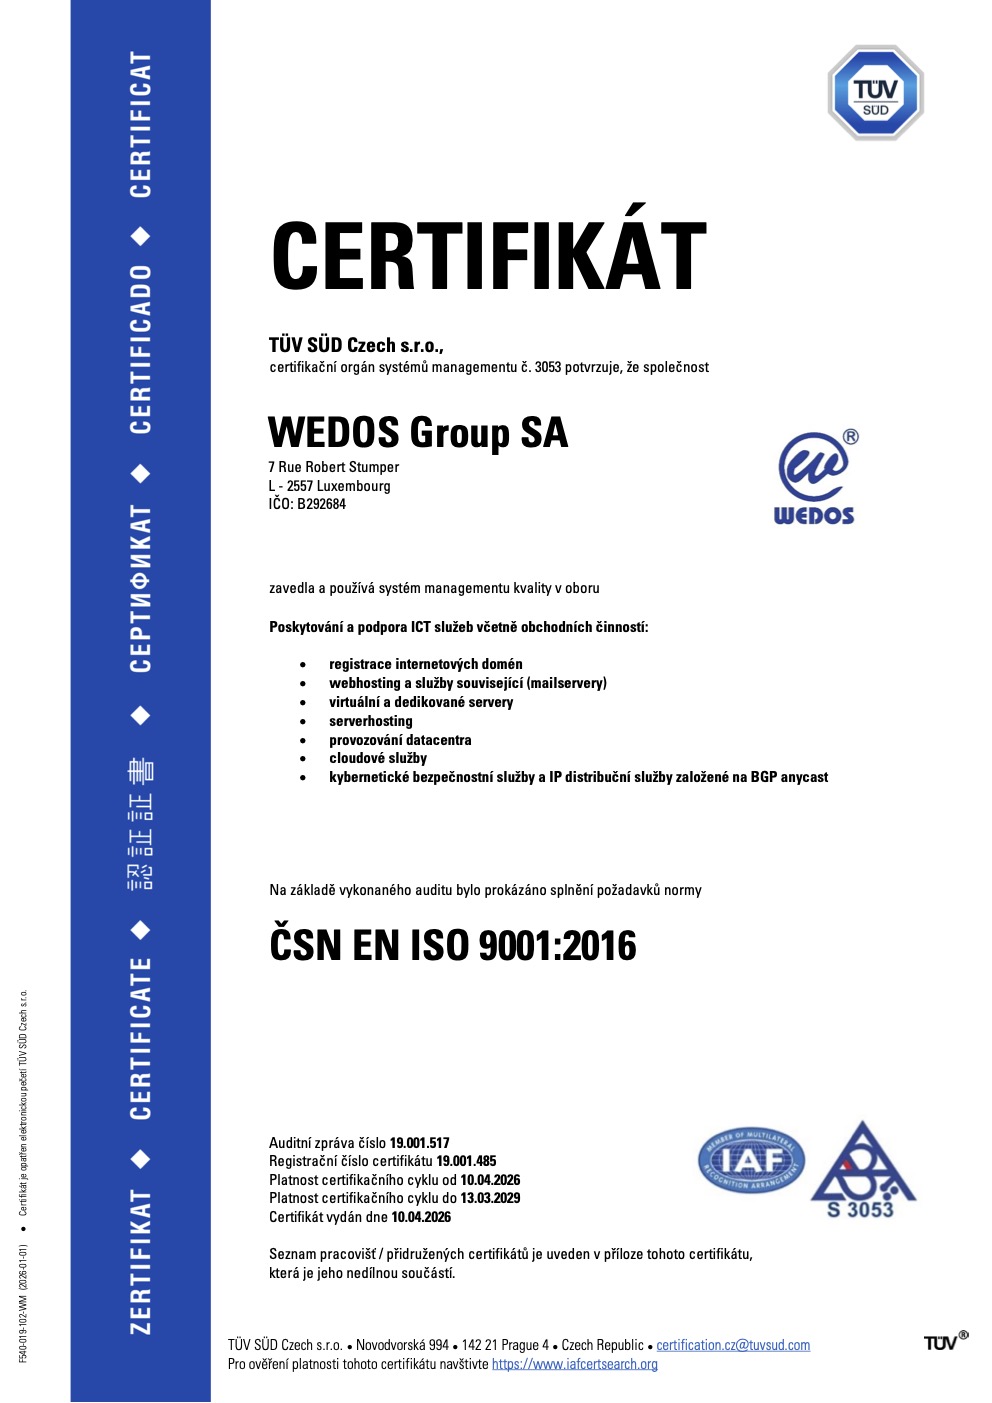
As the first, we decided back in 2011 to obtain the certifications ISO 9001 (quality management system) and ISO 14001 (environmental management system). We chose these certifications because we care about the environment, which is why, for example, we buy special energy-efficient processors for our servers. Later, in 2013, we added ISO 27001(information security management system), i.e. an ISO focused on information security. This ISO 27001 certification from TÜV SÜD focuses on a systematic approach to managing the security of confidential information, covering employees, processes, IT systems, and even the company’s strategy.

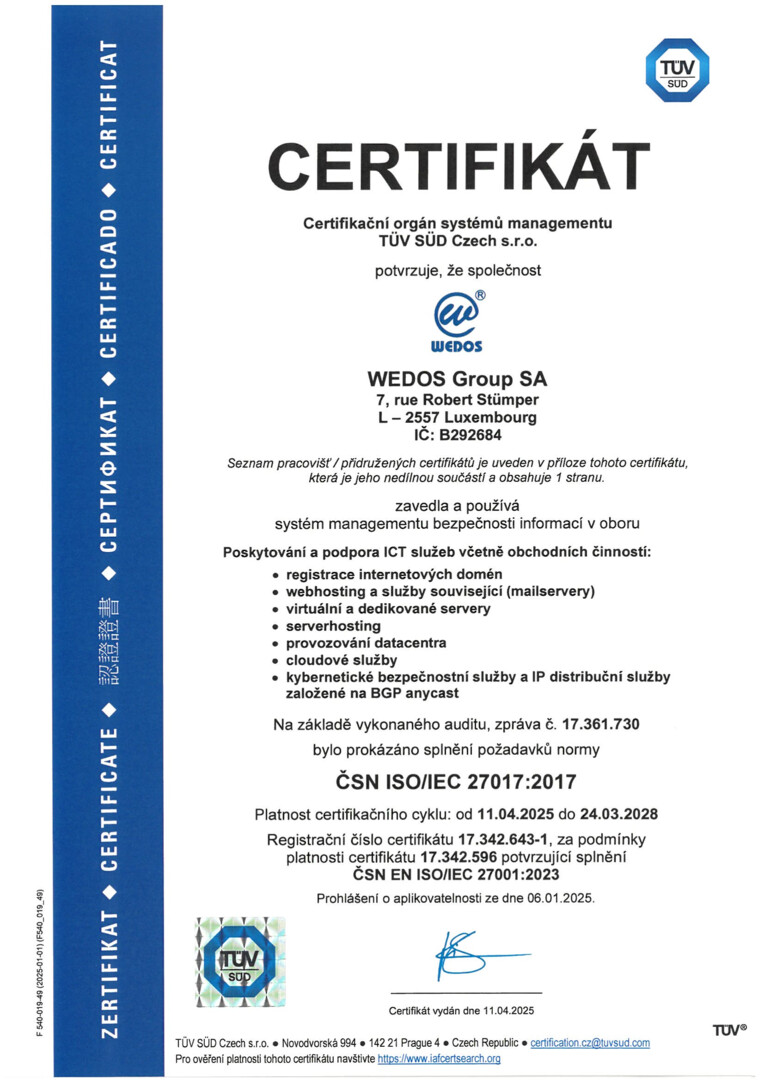
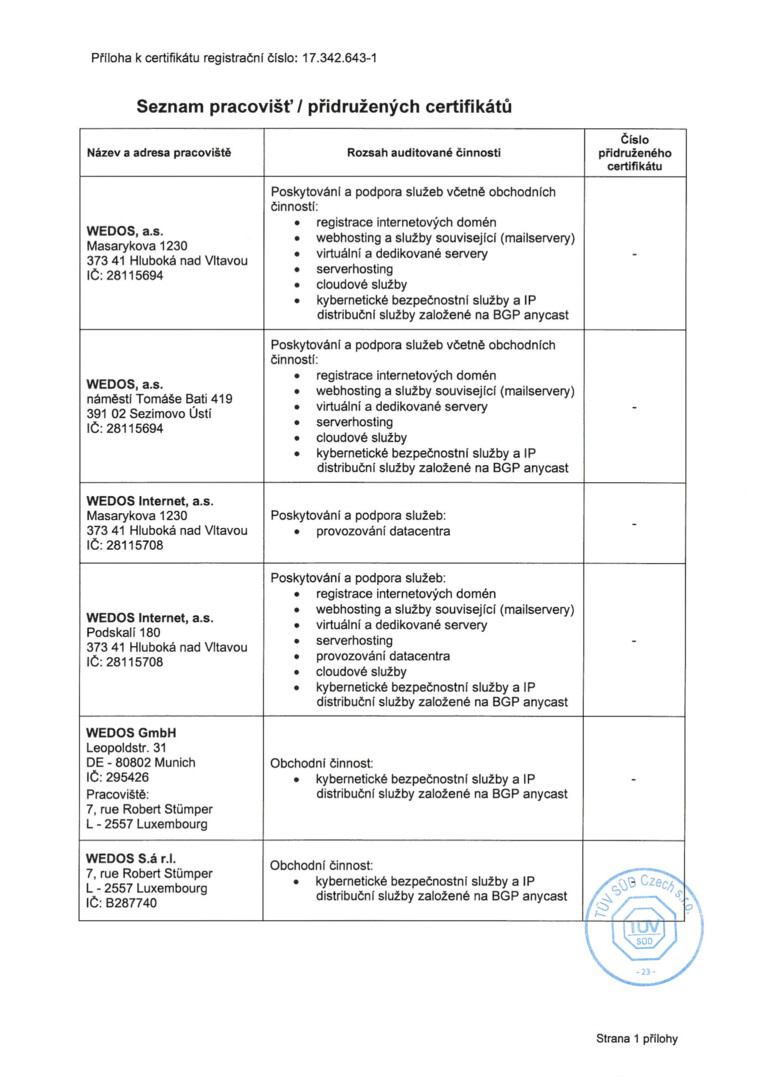
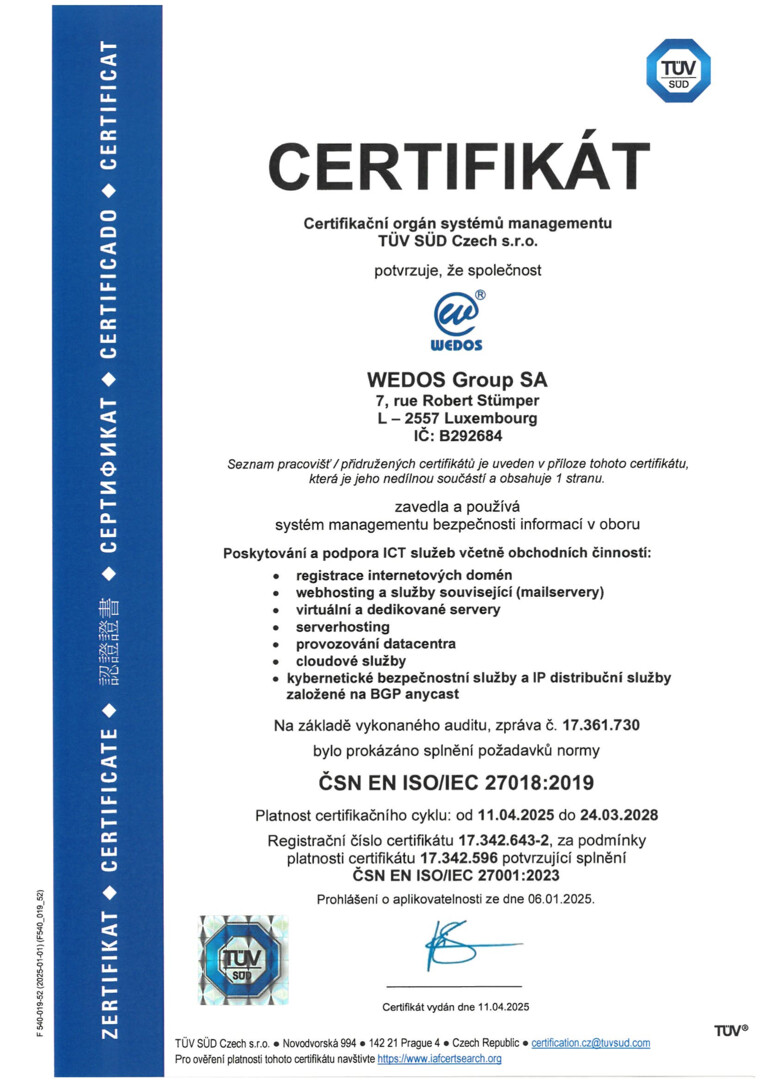
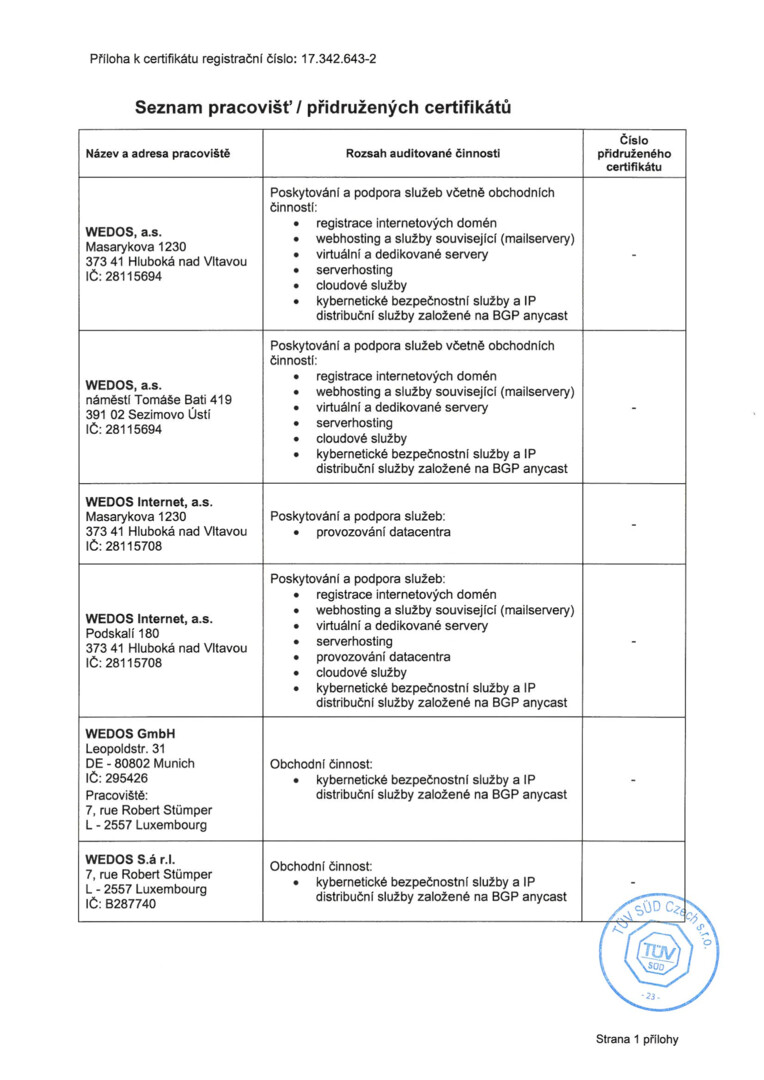
As one of the few companies in the Czech Republic, we obtained two more important certifications at the beginning of 2021. These are ISO 27017 (a set of practices for information security controls for cloud services) and ISO 27018 (a set of practices for protecting personally identifiable information in public clouds). Both certifications extend ISO 27001 and are focused on cloud services.
iso min 4

ISO 9001

Brings stabilized and consistent quality of the services provided.
The entire company and all of its processes are built on compliance with legal standards.
All processes and activities within the company follow an order based on predefined rules.
We have preventive measures in place to avoid defects and outages in the services we provide. 

ISO 14001

Demonstrates our positive relationship with the environment.
We take environmental protection and the prevention of environmental damage seriously in our company.
All our actions aim to minimize the impact of our activities on the environment.
We prevent any damage to the environment.

ISO 27001

This certification demonstrates that we can systematically identify information security risks and minimize them.
We have business continuity management plans in place for emergencies caused by humans or nature.
We have better protection of confidential information and reduce the risk of hacker attacks.
We can cope more quickly with the consequences of an attack, and we improve our systems’ ability to overcome the consequences of emergencies.
We have established a structured and globally recognized information security methodology.
We are in compliance with legal and contractual requirements.

ISO 27017

Defines roles and responsibilities in the cloud environment.
Ensures clear and secure rules for removing all data from the cloud.
Ensures rules for separating customer services in a virtual environment.
Defines both software (cloud) security and hardware (physical) security.
Defines how cloud services are monitored.

ISO 27018

Provides higher security for personal data and information.
Guarantees transparency in the use of personal data.
Sets rules for transferring data to subcontractors.
Complies with all legal standards.

Scroll to Top